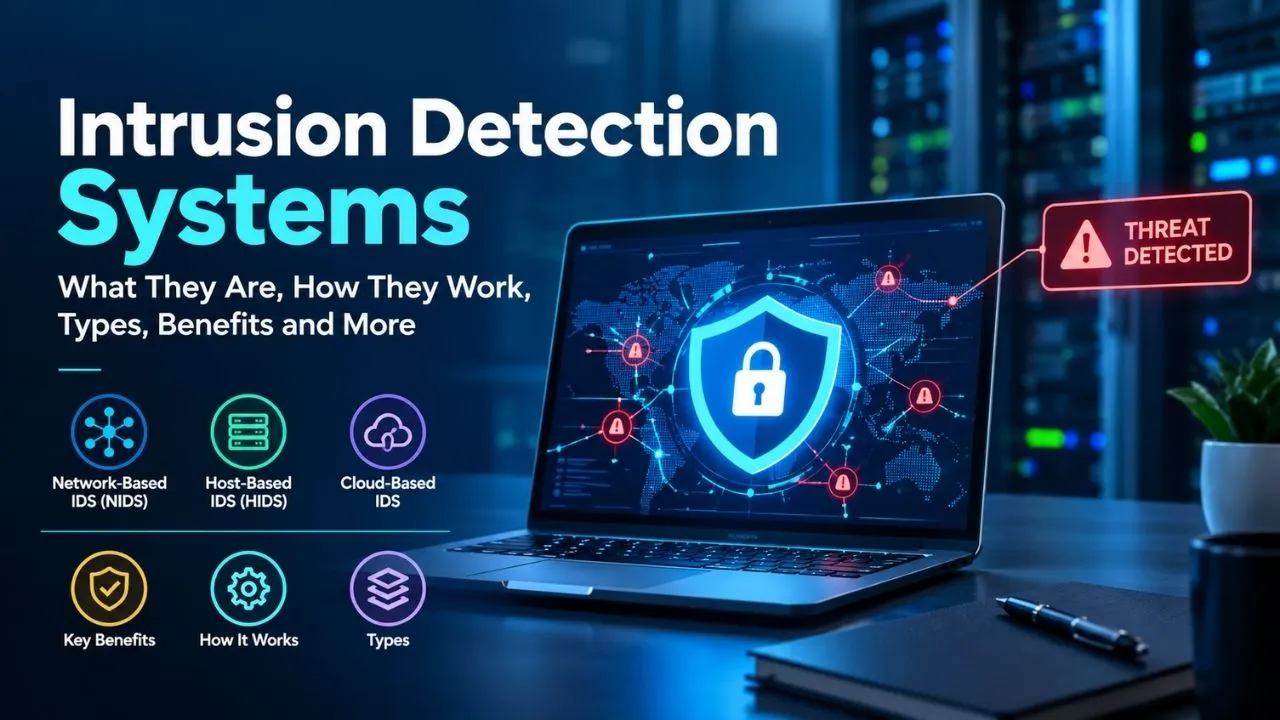
Cyberattacks are becoming increasingly sophisticated, making it difficult for organizations to rely only on traditional security tools such as firewalls and antivirus software. Businesses need continuous visibility into what is happening across their networks, servers, applications and endpoints. This is where intrusion detection systems (IDS) play an important role.
An IDS monitors network traffic or system activity, identifies suspicious behavior, and generates alerts when it detects a potential security threat. Unlike a firewall, which primarily controls whether traffic is allowed or blocked, an IDS focuses on detecting activity that may indicate an attack, policy violation or unauthorized access.
Modern security environments can combine IDS with security information and event management (SIEM), intrusion prevention systems (IPS), endpoint security and other technologies to create a layered defense strategy.
What Are Intrusion Detection Systems?
So, what are intrusion detection systems?
Intrusion detection systems are cybersecurity tools designed to monitor network traffic, devices or host activity for signs of malicious behavior, unauthorized access and security-policy violations. When an IDS identifies suspicious activity, it generally records the event and sends an alert to security administrators or a centralized security platform.
For example, suppose an employee’s account suddenly generates hundreds of failed login attempts or a server begins communicating with an unusual external address. An IDS can recognize the activity as suspicious and alert the security team for investigation.
An IDS can be deployed as dedicated hardware, software installed on endpoints or servers, or as a cloud-based security service. Depending on its deployment, it can monitor an entire network or focus on a particular host or application.
One important point is that a traditional IDS is primarily a detection and alerting technology. It does not necessarily stop an attack automatically. Prevention generally requires an IPS or another security control.
How Does an Intrusion Detection System Work?
The basic operation of an IDS can be explained through a series of steps:
1. Data Collection
The IDS first collects information from network traffic, packets, system logs, applications, files, processes or other monitored sources.
A network-based IDS may inspect copies of traffic flowing across a network, while a host-based IDS collects information directly from an endpoint or server.
2. Traffic and Activity Analysis
The collected information is analyzed to determine whether the activity resembles known malicious behavior or deviates significantly from normal behavior.
The analysis may involve attack signatures, statistical models, behavioral baselines, protocol analysis or other detection techniques.
3. Threat Identification
When suspicious activity matches a detection rule or exceeds an established threshold, the IDS identifies it as a potential intrusion.
For example, it could detect repeated login failures, port scanning, suspicious file changes, abnormal network traffic or attempts to exploit a known vulnerability.
4. Alert Generation
The IDS generates an alert containing information about the suspected event. Depending on the system, an alert can include details such as the time, source, destination, activity type and severity.
These alerts can be sent directly to security personnel or forwarded to a SIEM platform for centralized analysis.
5. Investigation and Response
The security team investigates the alert and determines whether it represents a genuine threat or a false positive. If necessary, administrators can isolate a device, block an address, terminate an account or begin a formal incident-response process.
This human or automated response is what turns detection into effective security operations.
Types of Intrusion Detection Systems
Intrusion detection systems can be categorized according to where they operate and what they monitor.
Network-Based Intrusion Detection System (NIDS)
A Network Intrusion Detection System monitors network traffic across a particular network segment or environment. It can inspect traffic for suspicious packets, attack signatures, scanning activity and unusual behavior.
NIDS deployments can be positioned at strategic locations, such as behind firewalls or between network segments. Many network IDS implementations analyze copies of network traffic rather than sitting directly in the communication path.
NIDS is particularly useful for organizations that need visibility across multiple devices.
Host-Based Intrusion Detection System (HIDS)
A Host Intrusion Detection System is installed on an individual device such as a server, workstation or other endpoint.
Rather than examining an entire network, HIDS focuses on activity occurring on the host. It can monitor system logs, file changes, processes, access attempts and other system events.
For example, if important system files are unexpectedly modified, a HIDS can detect the change and notify the security team.
Protocol-Based IDS
A Protocol-Based Intrusion Detection System focuses on specific communication protocols. It can be deployed around servers and monitor protocol interactions for suspicious behavior.
Application Protocol-Based IDS
An Application Protocol-Based IDS operates at the application layer and monitors application-specific communications. It can be useful for identifying threats such as suspicious requests or attacks targeting web applications and databases.
Hybrid IDS
A hybrid IDS combines multiple monitoring approaches, such as network-based and host-based detection. Combining different sources can provide a broader view of an organization’s security environment.
Intrusion Detection Methods
The effectiveness of an IDS depends heavily on how it identifies threats. The two most common detection approaches are signature-based and anomaly-based detection. Hybrid approaches can combine both.
Signature-Based Detection
Signature-based detection searches for known patterns associated with previously identified attacks.
An IDS maintains a database of signatures representing known malicious activity. When observed traffic or system activity matches a signature, the IDS generates an alert.
The main advantage is accuracy when dealing with known threats. However, signature-based detection can struggle with new attacks for which no signature exists. Keeping signature databases updated is therefore important.
Anomaly-Based Detection
Anomaly-based detection establishes a baseline for normal network or system behavior and then looks for significant deviations from that baseline.
For instance, if a server normally sends a small amount of traffic but suddenly starts transferring unusually large amounts of data, the behavior may be flagged as suspicious.
Anomaly detection can help identify previously unknown attacks and potentially zero-day threats. However, unusual does not always mean malicious. Legitimate changes in user or network behavior can produce false positives.
Hybrid Detection
Hybrid IDS combines signature-based and anomaly-based methods. Known threats can be detected through signatures, while unusual behavior can be identified through behavioral analysis.
This approach can provide broader coverage than relying exclusively on one detection technique.
Major Components of an IDS
Although implementations differ, a typical intrusion detection system contains several important components.
Sensors: Sensors collect network packets, system logs, file activity, processes and other security-related information.
Analysis engine: This is the core component that evaluates collected data and searches for suspicious patterns or deviations.
Detection database: It may contain attack signatures, security rules, behavioral information and other threat intelligence.
Alerting system: Once suspicious activity is detected, the alerting mechanism communicates the event to administrators or security platforms.
Management interface: Security teams use the management interface to configure rules, review alerts and investigate historical activity.
Stamus Networks similarly describes sensors, an analysis engine, alert generation, management functions and a knowledge base as important parts of an IDS architecture.
What Can Intrusion Detection Systems Detect?
Depending on their configuration and capabilities, IDS solutions can identify many different forms of suspicious activity, including:
- Port scanning
- Brute-force login attempts
- Malware-related activity
- Denial-of-service attacks
- Attempts to exploit known vulnerabilities
- Suspicious network connections
- Unauthorized access
- Unusual traffic patterns
- Suspicious file modifications
- Policy violations
- Certain forms of data exfiltration
- Application-layer attacks
For example, GeeksforGeeks identifies threats such as malware, port scanning, DoS/DDoS attacks and brute-force attacks among the activities IDS technologies can detect.
Benefits of Intrusion Detection Systems
Improved Network Visibility
An IDS provides security teams with additional visibility into traffic and system behavior. This can be especially valuable when attackers bypass perimeter controls.
Faster Threat Detection
Automated monitoring can identify suspicious activity faster than relying exclusively on manual log analysis.
Support for Incident Response
IDS alerts and logs provide useful evidence for investigating security incidents and understanding how suspicious activity occurred.
Detection of Policy Violations
IDS technology can identify activity that violates an organization’s security policies, even when the activity is not necessarily associated with malware.
Better Security Monitoring
When connected to a SIEM, IDS alerts can be correlated with information from firewalls, endpoints, identity systems and other security tools. This can help security teams prioritize important incidents and reduce investigation time.
Compliance Support
IDS capabilities can also support certain compliance requirements. IBM notes that some regulatory frameworks, including PCI DSS, require organizations to implement intrusion detection measures.
IDS vs Firewall
An IDS and firewall are complementary rather than interchangeable technologies.
A firewall primarily controls network traffic according to predefined policies. It can allow or block connections based on factors such as source, destination, port and protocol.
An IDS, on the other hand, observes activity and looks for evidence of suspicious or malicious behavior. It generally alerts administrators rather than automatically blocking the detected traffic.
In simple terms:
Firewall = controls access
IDS = detects suspicious activity
Using both provides stronger protection than relying on either technology alone.
IDS vs IPS
One of the most common cybersecurity questions is the difference between an IDS and an IPS.
An Intrusion Detection System primarily detects and reports suspicious activity.
An Intrusion Prevention System (IPS) goes a step further by actively taking action against detected threats. Depending on its configuration, an IPS may block malicious traffic, terminate connections or trigger other defensive actions. IPS technologies are commonly deployed inline so that traffic passes through the security control.
| Feature | IDS | IPS |
| Primary purpose | Detect threats | Detect and prevent threats |
| Typical operation | Passive/out-of-band | Inline |
| Automatic blocking | Generally no | Yes |
| Main output | Alerts and logs | Alerts plus prevention actions |
| Risk of disrupting traffic | Lower | Higher if incorrectly configured |
What Are Intrusion Detection and Prevention Systems?
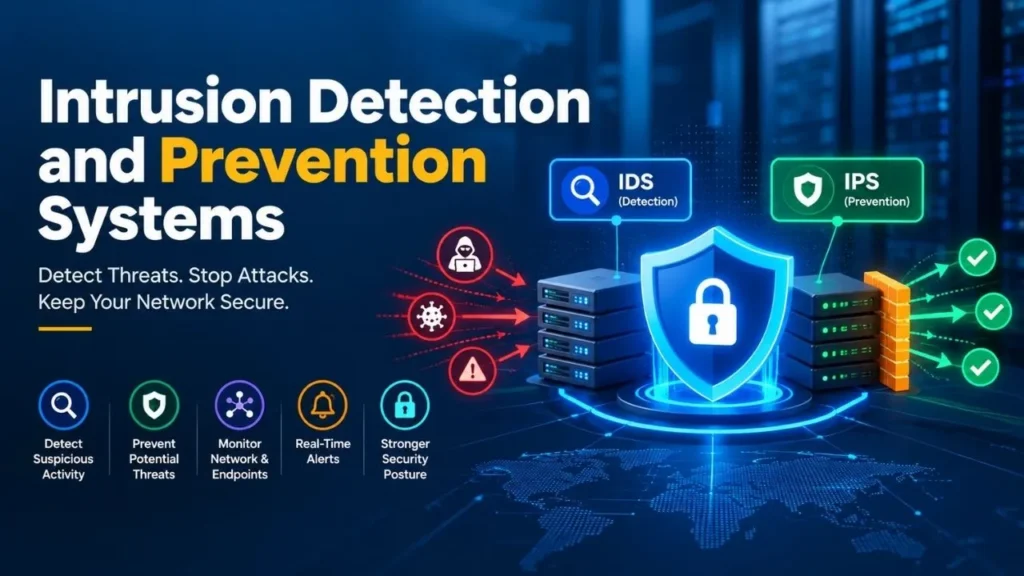
Intrusion detection and prevention systems (IDPS) combine detection and prevention capabilities into a broader security solution.
An IDPS can identify suspicious activity, record security events, alert security teams and automatically respond to certain threats. IBM notes that IDS and IPS capabilities are frequently combined into a single intrusion detection and prevention system.
This approach is useful for organizations that need both visibility and automated protection.
However, automation must be carefully configured. An overly aggressive prevention policy could block legitimate traffic, while weak policies may fail to stop an actual attack.
Limitations of Intrusion Detection Systems
Despite their benefits, IDS technologies are not a complete cybersecurity solution.
One major challenge is false positives. Legitimate activity that differs from normal behavior may trigger an alert. If an organization generates too many alerts, security analysts can experience alert fatigue.
IDS systems can also face evasion techniques. Attackers may use encryption, fragmented packets, spoofing or other methods to make malicious activity harder to identify. IBM highlights fragmentation, encryption, spoofing and deliberate alert generation among techniques that can challenge IDS deployments.
Another limitation is that a traditional IDS generally does not stop an attack by itself. Detection must be followed by investigation and response, unless the IDS is integrated with prevention or automated response capabilities.
How to Improve IDS Effectiveness
Organizations can improve the effectiveness of their IDS by following several practices:
- Keep signatures updated so known threats can be identified.
- Tune detection rules to reduce unnecessary alerts.
- Establish accurate behavioral baselines for anomaly detection.
- Integrate IDS with SIEM platforms for centralized monitoring.
- Combine network and host monitoring where appropriate.
- Prioritize alerts based on severity and asset importance.
- Regularly review detection performance and update rules.
- Connect detection with an incident-response process.
The goal should not simply be to generate as many alerts as possible. Effective IDS deployment is about producing useful, actionable security intelligence.
Read More Related Blogs: How to Secure a WordPress Site | Is Dailymotion Safe | What Is a VPN vs Proxy | What is VPN Encryption
Final Thoughts
Intrusion detection systems are an important part of modern cybersecurity because they provide visibility into suspicious network and system activity that other security controls may miss. NIDS can monitor network traffic, while HIDS can provide detailed visibility into individual endpoints. Signature-based detection is effective against known threats, while anomaly-based detection can help identify unusual or previously unseen behavior.
However, an IDS should not be considered a standalone defense. Firewalls, endpoint protection, SIEM, threat intelligence, incident response and intrusion prevention technologies can complement its capabilities. Organizations that combine detection with appropriate prevention and response measures can build a stronger and more resilient security architecture.
For businesses dealing with sensitive data, critical applications or complex networks, understanding what are intrusion detection systems, how they work and how they fit into intrusion detection and prevention systems is essential for developing an effective cybersecurity strategy.
FAQs
An IDS is a security tool – hardware, software, or a cloud-based service — that monitors network traffic or system activity for signs of malicious behavior, unauthorized access, or policy violations, and generates alerts when it detects a potential threat.
An IDS collects data from network traffic or system logs, analyzes it using signature-based or anomaly-based methods, identifies suspicious activity that matches known attack patterns or deviates from normal behavior, and generates an alert for security teams to investigate.
A firewall controls access by allowing or blocking traffic based on predefined rules. An IDS, on the other hand, monitors and detects suspicious activity that may already be happening on the network, then alerts administrators rather than blocking traffic automatically.
An IDS detects and reports suspicious activity but does not block it. An Intrusion Prevention System (IPS) goes further by actively blocking malicious traffic, terminating connections, or taking other automated defensive actions.
The two primary types are Network-Based IDS (NIDS), which monitors traffic across a network, and Host-Based IDS (HIDS), which monitors activity on an individual device. Protocol-based, application protocol-based, and hybrid IDS are other variations.
Signature-based detection matches activity against a database of known attack patterns, making it accurate for known threats but less effective against new ones. Anomaly-based detection establishes a normal behavior baseline and flags significant deviations, which can catch unknown or zero-day threats but may produce more false positives.
An IDS can detect port scanning, brute-force login attempts, malware activity, denial-of-service attacks, exploitation attempts, unauthorized access, suspicious file modifications, policy violations, and certain forms of data exfiltration.
IDS technologies can generate false positives, leading to alert fatigue. They can also be evaded through techniques like encryption, traffic fragmentation, or spoofing, and a traditional IDS does not stop an attack on its own — it requires investigation and response, or integration with a prevention system.
An IDPS combines detection and prevention capabilities into one system — it can identify suspicious activity, alert security teams, and automatically respond to certain threats, such as blocking malicious traffic.
Yes, in some cases. Certain regulatory frameworks, such as PCI DSS, require organizations to implement intrusion detection measures as part of their security compliance requirements.